
- This document is intended to be paired with Cloud Streaming - SSO - SAML Configuration for users with Google Admin Console to manage their users.
You must start an SSO Configuration on your Cloud Portal Admin to continue below. It is best to configure both ends of this SAML handshake together with 2 open windows or tabs on your browser.
Step 1 - Begin Google SAML Application Configuration
- Sign into the Google Admin Console (admin.google.com)
- Navigate to Apps / Web and mobile apps
- Click Add App and select Add custom SAML app in the drop down
- In the App details screen. add Digital Campus or Swank Cloud Streaming in the App name field
- In the Google Identity Provider Details screen, under Option 1: Download IdP metadata click Download Metadata and save for a later step, then click Continue
Step 2 - Configure Streaming Server SAML Authentication
- In a separate tab/window, login to your Swank Streaming portal with your registered Admin account.
- Select SSO Configuration from the left menu.
- Review the list of SSO Identity Providers configured for your portal
-
Legacy Providers: If you've previously configured SSO via SAML or Google OAuth, you'll find their configuration listed at the bottom here.
- Note: You cannot "upgrade" your existing SAML configuration to our new Identity Service host - you must create a new SAML configuration.
- The legacy configurations are deactivated automatically when a new SSO Identity Provider Configuration is activated. You can "fallback" to the legacy provider by deactivating the new provider(s).
-
SSO Configurations: At the top of the page, see the list of available providers. You can:
- Activate or Deactivate existing configurations via the Active toggle.
- Edit or Delete existing configurations via button actions
- Add new SSO Identity Providers via the button at the Top. (We'll continue this guide from this route)
- Click Add Configuration
- Choose the Provider Type of SAML
- Enter a Display Name - This displays on the list of SSO Configurations as well as the button added to the Login page. (Suggested: Google SAML)
- Select Upload SAML Metadata File and select the file downloaded in step 1.1.5
- Toggle Require Valid Metadata to the off position if needed.
- Toggle Require Valid Metadata to the off position if needed.
- Click the Save button to generate your SAML configuration.
- Complete the SAML handshake:
- These values will be presented for you to copy and enter back into your SAML Identity Provider's configuration.
- SP EntityID - Required
- SP Metadata URL - Optional (Google does not support)
- Callback Path (ACS Endpoint) - Required
- Once these values are saved at the Identity Provider end, the SAML handshake between your Portal and your Identity Provider should be complete.
- When copying and pasting this info, make sure there is no trailing "/" or spaces on the G suite side. This will result in errors. You must include the whole URL including the unique IDs redacted above
- These values will be presented for you to copy and enter back into your SAML Identity Provider's configuration.

Step 3 - Complete Google SAML Application Configuration
- Copy Callback Path (ACS Endpoint) to the ACS URL field in your Google SAML App configuration
- Copy SP EntityID to the Entity ID field in your Google SAML App configuration
- Name ID format = EMAIL
- Name ID = Basic Information > Primary email
-
Start URL and Signed response checkbox will not be required
- Click Continue
- On the Attributes Screen click ADD MAPPING and enter the details below. Renaming the attributes to match standard expected values for the portal:
- Google Directory attributes: --> App attributes:
-
Required
- Primary email --> email
-
For Instructor/Admin accounts the following are required:
- First Name --> given_name
- Last Name --> family_name
- Click Finish
- User access should be enabled for the appropriate organizational units.
- Access can be modified under Apps > Web and mobile apps
- Click on the Swank SAML App you created to open for editing.
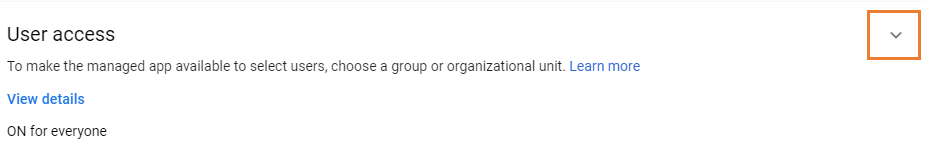
- Expand the user access section by clicking the expansion icon in the upper right corner.
- You can turn on for everyone to test initially and if desired you can scale back access later.

Step 4
Role Mapping, User Authorization, and Permission Elevation
All successful authentications will be authorized at the "Basic" or "User" account levels (role) by default depending on the portal settings. To elevate permissions to a higher permission level for Instructors or Administrators you will need to add Role Mappings to grant this elevation either by Attribute Value or Individual UserID. For more information on Account Level Permissions, please see the following article:
https://swankmp.zendesk.com/hc/en-us/articles/5723258435092-Cloud-Streaming-User-Account-Roles
There are 3 methods of providing roles and are respected in the following order - with the former values overriding any latter options.
- Mapping Roles on the Streaming Portal
- Claim/Attribute of "role" directly provided by your Identity Provider
- The Portal Default "User" or "Basic" role (Set by your Swank support)
Option 1: Mapping Roles on the Streaming Portal (Recommended)
Initial Account Creation
A registered account with the preferred role using the email of a user can be established prior to their initial login by using one of the methods described in the link below.
Post Account Creation
Individual Role Mappings can be modified after an account has been established by using the following steps:
- Log in to your streaming portal with an Admin account.
- Select Users from the menu
- Select the expand menu for the intended user and select Edit Profile
- Select the appropriate Role and click Save
Option 2: Identity Provider Role Assignment
In some cases, your Identity Provider can provide a Claim or Attribute for each User with the Name of "role" and the Value of one of our available user roles: "Admin", "Instructor", "User", or "Basic". This allows your Identity Provider Admin to set the roles based on policies and rules aligned with your organizations larger technology access strategy and to manage that access centrally at your User Directory.
Each Identity Provider has a different method for handling this action, please consult your identity provider to confirm the availability and documentation.
Notes:
- The attribute name is case-sensitive and must be "role".
- The attribute values are not case-sensitive.
- You can verify you have the "Role" attribute provided by checking your diagnostics while logged in under the desired SSO setup.
- Log into your Portal's catalog, appending /diagnostics to the URL.
-
For Example:
- https://digitalcampus.swankmp.net/[your site ID]/diagnostics
- https://streaming.swankmp.net/[your site ID]/diagnostics)
-
For Example:
- Look for the field Swank.ExternalRole for the role sent by your identity provider (IDP).
- Log into your Portal's catalog, appending /diagnostics to the URL.
- Once an account is established on your Swank Streaming portal it cannot be overwritten by your IDP role. You can do one of the following:
- Update the account role manually in the streaming portal.
- You can attempt to remove the established account, but if it has been used with the title request process this is not always possible.
Option 3: Portal Default Role
All successful authentications will be authorized at the "Basic" or "User" account levels (role) by default depending on the portal settings.
Final Step
Make Configuration Active
Once you configured your SAML Identity Provider, and determined your User's roles, remember to click the Activate toggle on the SSO Configuration page for your chosen Provider(s). If you are currently viewing the SSO Configuration detail page, you can click the "Go Back" link at the top of the page or click SSO Configuration from the side menu.
- Toggle Active to the On position for your new SSO Configuration.
-
Comments
0 comments
Please sign in to leave a comment.